
SBI Confirms Cyberattack, Nearly 3,900 Customer Records Reportedly Exposed on Dark Web
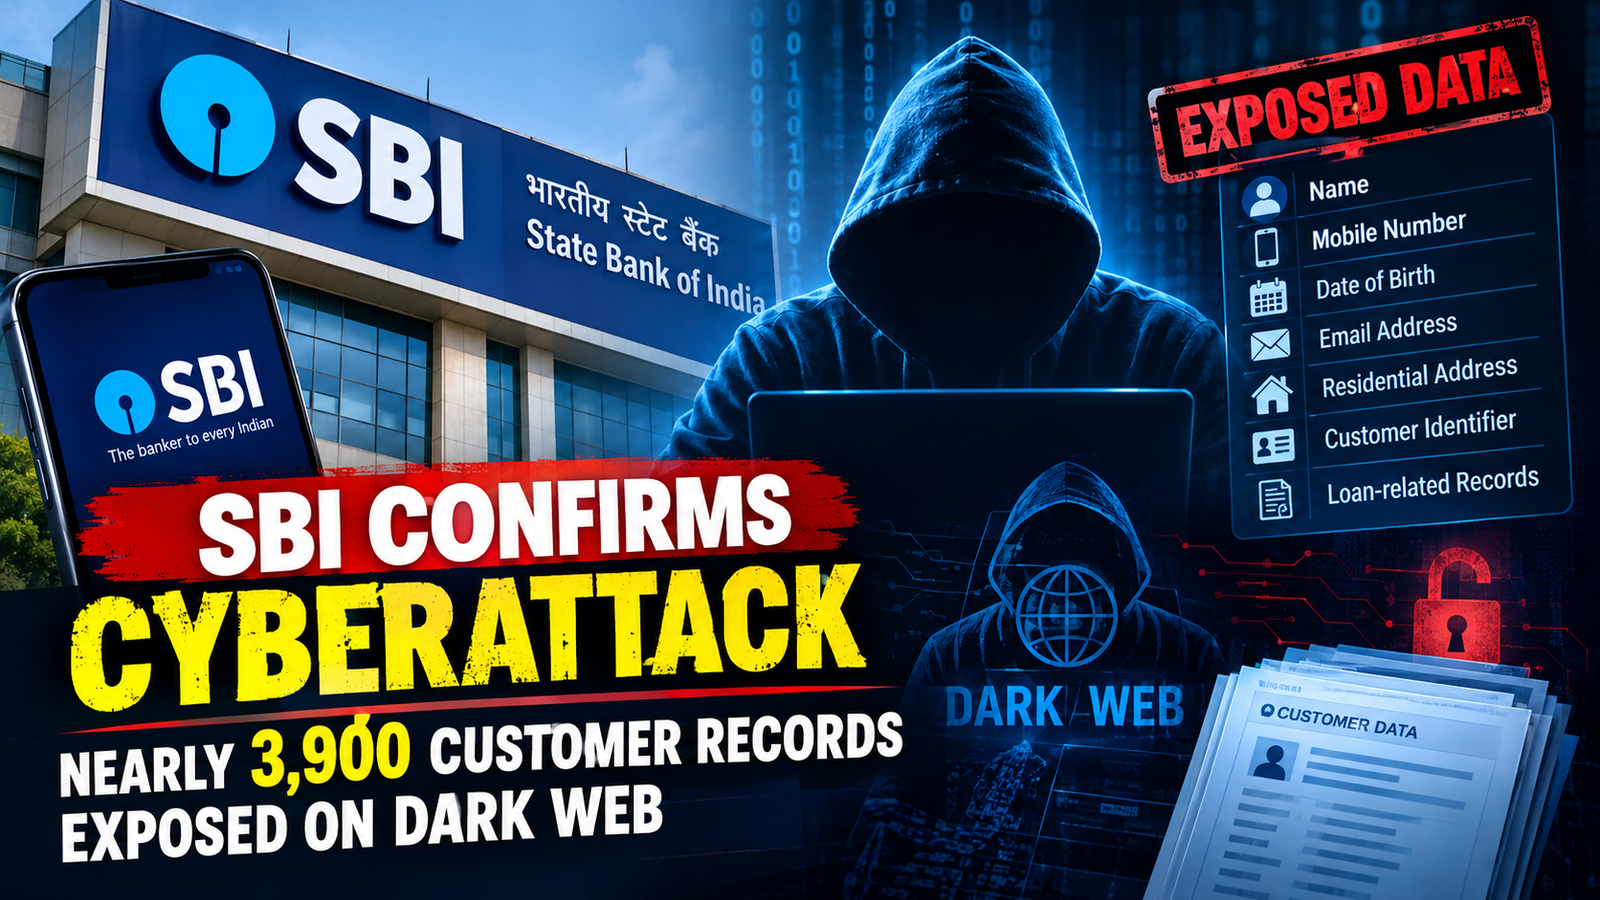
Mumbai, October 21: The State Bank of India (SBI), the country’s largest public sector lender, has reported a cybersecurity incident involving the exposure of nearly 3,900 customer records on the dark web, raising concerns over the protection of sensitive banking-related information and the growing threat of cybercrime.
According to reports, SBI identified 3,897 customer records that were allegedly exposed online. The information reportedly includes personal details such as customers’ names, mobile phone numbers, dates of birth, email addresses, residential addresses, customer identifiers and certain loan-related records.
The incident has drawn attention to the risks posed by cyberattacks and the unauthorised circulation of personal information on underground online platforms. Such data can potentially be misused by cybercriminals to carry out identity theft, targeted phishing campaigns, impersonation and financial fraud.
Investigation Underway
SBI has reportedly initiated an investigation into the incident with assistance from an independent cybersecurity agency. The inquiry is expected to examine the nature of the exposed records, the circumstances surrounding their appearance on the dark web and whether the information could have been accessed through a security vulnerability or another unauthorised channel.
The bank’s reported assessment indicates that its core banking operations remain unaffected by the incident. However, the exposure of personal information remains a serious concern because criminals can use genuine customer details to make fraudulent calls, send deceptive messages and create convincing scams.
The precise source of the data and the full extent of any potential compromise will depend on the findings of the investigation. The number of records identified in the preliminary assessment should also be distinguished from broader claims about datasets allegedly associated with the bank or its subsidiaries.
Customers Advised to Remain Alert
Cybersecurity experts generally advise bank customers to exercise caution when receiving unexpected calls, text messages, emails or instant messages claiming to be from bank officials. Fraudsters may use leaked personal information to make their communications appear genuine and persuade victims to disclose confidential credentials.
Customers should never share their one-time passwords (OTPs), ATM PINs, internet banking passwords or other authentication details with anyone. They should also avoid clicking suspicious links, downloading unverified applications or responding to messages demanding immediate action on their bank accounts.
Any suspicious transaction or suspected attempt at fraud should be reported promptly through the bank’s official customer-service channels. Customers should use verified contact details available on the bank’s official website rather than numbers supplied in unsolicited messages.
Data Security in Focus
The reported incident highlights the continuing challenges faced by financial institutions as cybercriminals increasingly target personal and financial information. Banks must continually strengthen their security systems, monitor unusual activity, investigate suspected breaches and communicate clearly with customers when their information may be at risk.
For SBI, the investigation will be important in establishing how the records became available online and what additional safeguards may be necessary.
While the reported exposure does not automatically mean that customers’ accounts have been compromised or that money has been stolen, it underscores the importance of vigilance. Customers should monitor account activity and remain alert to suspicious communications while the investigation continues.
The full scope and origin of the exposed records remain subject to verification as the inquiry progresses.
*AI Generated
Powered by Froala Editor